OSSTMM
Security testing should produce knowledge, not theater.
Historical context
The Open Source Security Testing Methodology Manual (OSSTMM) from ISECOM organizes security testing around operational methodology, trust analysis, human/physical/wireless/telecommunications/data-network channels, and reporting.
Founder lens
I respect OSSTMM because it tries to make security testable and reportable. “Secure” is not a mood. In XERXES projects the corresponding instinct is evidence-first qualification: define the boundary, test the behavior, retain the result, and do not confuse a checklist with truth.
What carries into XERXES
Keep exploring // human pathways
Continue through adjacent ideas, products, principles, and historical lineages. These pathways preserve the relationships in the underlying knowledge graph while keeping exploration natural for a human reader.
A broad, source-linked systems lineage behind XERXES SI: operating systems, networks, telephone infrastructure, hacker culture, radio, optics, acoustics, biology, security methodology, hardware, workstations, and the physical culture of technical discovery.
CONTINUE →lineage2600 community2600 and earlier phone-phreaking stories sit inside a broader hacker lineage: curiosity about systems, telecommunications literacy, public discussion, community, and the ethical question of what responsible exploration should become.
CONTINUE →lineageAcoustics + sound systemsAcoustics is cross-domain systems engineering: pressure waves become measurements, electrical signals, digital representations, room behavior, interfaces, speech, music, alerts, and subjective experience.
CONTINUE →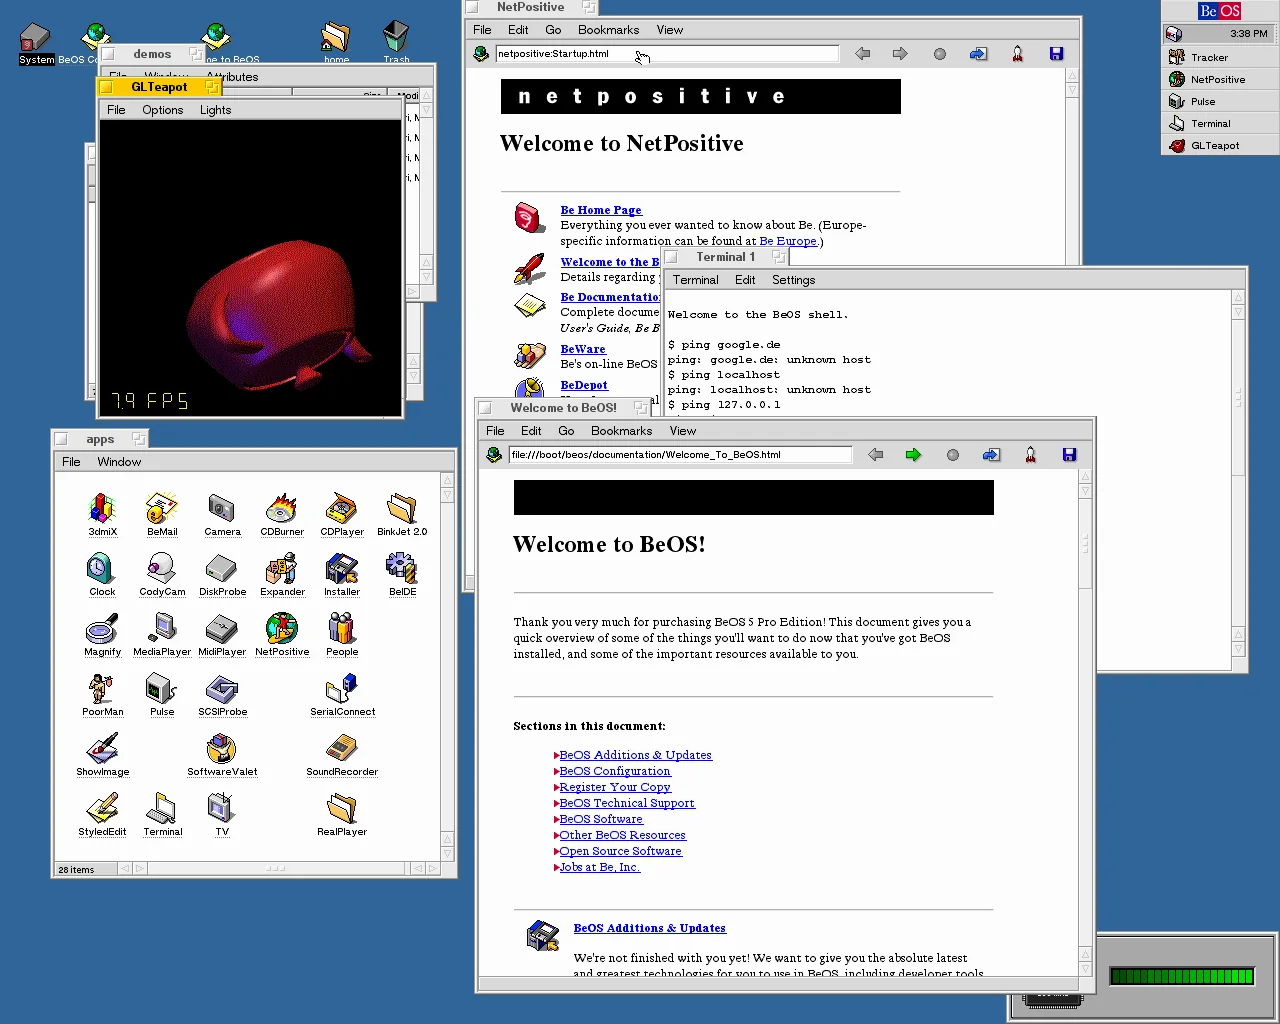 lineageBeOS
BeOS is preserved as an alternative-systems case study: a multimedia-oriented, multiprocessing desktop that made responsiveness and coherence visible when the personal-computing mainstream was taking other paths.
CONTINUE →